Online security – a buzzword we hear echoing in news campaigns, in notifications from our banks, or whenever we read an article about another data breach. A buzzword that, as our parents used to say, goes in one ear and out the other… and we do nothing about all this "security." It's time to change that and stop crying… like a Pole after the event! How do you ensure website security?
Website Security – burglary is not the same as burglary
Can my website be hacked? Is my website worth hacking? The truth is, there's no place on the internet that isn't worth hacking into. Every domain and every website is a potential target for exploitation – placing links to various potency medications, redirecting to your own shady domain, or secretly using our server for mailings and serving content clearly intended for an adult audience to innocent internet users. The number of ways to exploit a compromised website is limited only by the hackers' creativity.
A website hijacking has various consequences, including problems with website performance and removal from the Google index due to optimization deletion. A hack also increases the risk of a website being removed from the SERPs as a result of penalties for inappropriate content or attacks. Even the best SEO can be seriously affected by such an attack. Furthermore, with each subsequent hack, the website loses credibility in the eyes of its users, and they become more hesitant to use the products and services offered. This lack of trust stems primarily from fear of losing one's personal data – user information is an attractive target for hackers. In some cases, website hijacking also entails significant costs, including revenue that could have been generated during the downtime. The costs of server cleanup and website restoration can also significantly impact a company's budget. Furthermore, there are legal ramifications.
Who is most at risk?
Every website and every person using the internet can become a victim of one of many types of cyberattacks. Hacks happen to large and well-secured companies:
(The rest of the article can be found below the form)
- In 2013, Adobe lost data – usernames and passwords, names and surnames, credit and debit card details – from 153 million accounts,
- LinkedIn lost user email addresses and passwords in 2012 and 2016,
- In 2020, Garmin lost access to a large portion of its systems and was forced to disable all services. To obtain the decryption key, the company decided to pay a ransom.
The scale of these breaches is much larger than what small website owners typically experience. However, this doesn't mean that security issues should be ignored or appropriate measures should be taken in the name of "prevention is better than cure."
Among the systems most susceptible to hacker attacks, popular CMSes like WordPress and Joomla are commonly cited. The frequency of hacks is influenced by factors such as the widespread installation of these solutions and a rather casual approach to software updates and security notifications. In the case of WordPress, plugins, which allow users to add new functionality to a website, are also a source of attacks. Some plugins are developed by third-party companies. Joomla's vulnerability manifests itself during system configuration, which tends to generate errors, and, similarly to WordPress, when installing external extensions.
You might like it
How to ensure website security?
Below are 6 basic elements that can help you increase your website's security and reduce careless behavior that can create risks.
- Password123, you guess!
Professional tools and the most sophisticated security programs can lose out to a lack of common sense and a lack of awareness of threats. I don't mean to suggest that modern solutions shouldn't be used – quite the contrary! I'm simply suggesting that we take a moment to reflect on our passwords. They are the ones most likely to fall prey to online thieves and wreak havoc on our virtual realms. The most common password-related sins include:
- Their simplicity – passwords like qwerty, 12345, abc123, or passwords related to the name of the service we have an account on. These types of security measures are easily cracked – firstly, they are quite intuitive, and secondly, they are among the most common ones found on lists of data stolen from various services,
- Their versatility—one password for everything? Such simple solutions work… for a short time. A data leak from one service can result in the loss of accounts in other spaces as well.
This infamous group also includes the unsightly habit of saving all passwords in one place – either in a notebook or in a plain text file located in a folder on your hard drive. While a traditional notebook might be attractive to a less agile thief, a file can be of interest to anyone who knows how to exploit the trust of users on public networks (e.g., Wi-Fi in a restaurant) – and from there, the path to taking over all our online selves is short.
So how can you ensure your passwords are secure? Some solutions that work well for both personal and corporate use are applications that allow you to securely store passwords, such as LastPass, 1Password, and their free equivalents, KeePass, and BitWarden. These solutions work similarly to the aforementioned password manager—they allow you to store your passwords in one place, but are significantly more secure. These programs generate incredibly complex passwords, which are then encrypted in various ways and stored in this form. Users only need a single password to access the application. These programs work not only on computers but also on mobile devices.
Another effective way to limit the possibility of account takeovers is multi-factor authentication. Implementing this solution requires verifying the user's login credentials in several ways, for example, using an app installed on the phone. This requirement to confirm the user's intent to access the account allows for additional control and the detection of unauthorized login attempts.
Passwords should also be changed from time to time, especially when there's a turnover among company employees. Whenever there's a change in the people responsible for various areas of online operations, it's a good idea to refresh access and ensure that only designated employees have access to password-protected areas.
- updates
Updating systems is another essential step in reducing the risk of unwanted activity on a website . This applies to all related elements – the CMS, server software, and plugins and extensions. Besides developing the application and adding new functionality, updates also address bugs and potential threats in existing code. Failure to update programs running on a website significantly facilitates its takeover by external users.
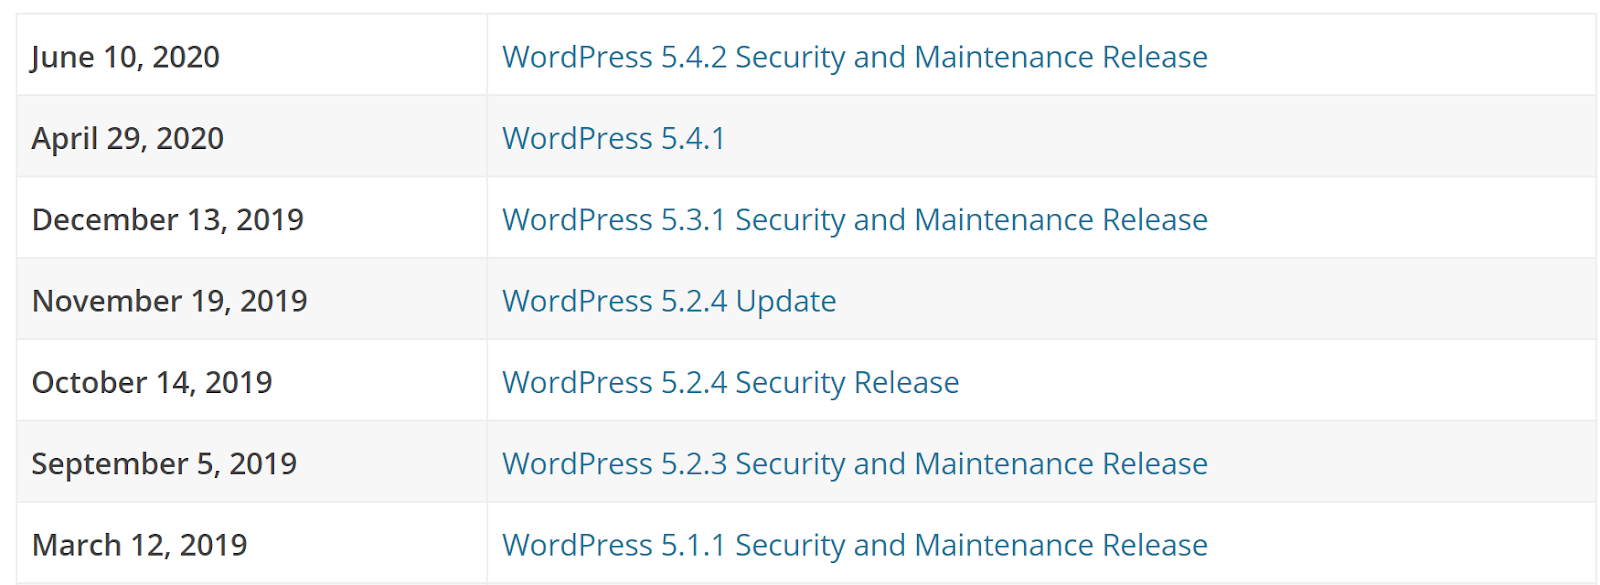
You can see how frequently security patches are implemented by analyzing the information provided with each software update. Most updates are accompanied by a blog post or release note detailing each patch.
Information about WordPress can be found at https://wordpress.org/news/

Joomla announces further updates here – https://www.joomla.org/announcements/release-news.html
Additionally, information regarding the need to update your CMS typically appears on the main page of the administration panel. Note: Updating older CMS versions (e.g., those that haven't been updated for several months) may result in issues with basic website functionality. Before starting the update, it's a good idea to prepare backups of your website files. It's best to update archaic CMS versions with the help of specialists, such as the software house responsible for the website's original appearance. The need to update the system running the website should be considered during the website design process , and update support should be included in the contract.
- Plugins and extensions
When discussing updates to popular CMSs, it's also worth considering the elements that expand the capabilities of these programs, such as plugins, extensions, and add-ons. Each of these programs offers new features for our CMS, unfortunately, not always the ones we care about. So how can we identify plugins that are safe? What should we look for?
Before installing an add-on to our CMS, it is worth taking a look at its popularity and reviews, checking the credibility of the company that released it, and making sure how often updates are made and what they concern.
It is a mistake to leave plugins unupdated – they are the ones that fix bugs and security holes that can be used to take over your online property.
- SSL
Implementing SSL isn't just a whim of your SEO or advertising specialist, but one way to improve the security of data flowing through your website. SSL, or more precisely, TSL, guarantees the confidentiality of data transmission and server authentication. It relies on asymmetric encryption with a public key, knowledge of which prevents decryption of the data. This requires a private key that is not shared externally. Key lengths in current TSL versions are at least 128 bits.
- Take care of your backup
Caution may add another item to your monthly website maintenance costs, but in times of crisis, it becomes invaluable. Website security isn't the first area you should skimp on. In this case, caution manifests itself through ensuring backups. Backups stored in a secure location reduce the risk of data loss. Securing databases and storing them in a separate location from the original files will ensure business continuity, even in the event of a failure or loss caused by a hack.
The hosting provider hosting the website will also store backups , which is very useful in the event of technical issues with the site – restoring the site to its previous state is usually a matter of a single phone call. Unfortunately, leaving the security of your websites in external hands doesn't always work, as customers of one Polish hosting company discovered in 2016.
- Educate yourself and your colleagues
Website security depends on many factors. The impact of some of these factors can be mitigated by educating everyone who works within them. Sometimes, simply brushing up on the basics of online security is enough – such as password creation, the need to use secure internet connections and log out after work, or being suspicious of unusual-looking emails.
A website is a sensitive area, and its vulnerability most often stems from our own ignorance. Maintaining the security of a website and all the resources essential to our business doesn't require specialized knowledge or technical skills—in many cases, implementing best practices is sufficient.
Frequently asked questions about website security
Implementing an SSL certificate is absolutely essential. It encrypts data sent between the user and the server (e.g., login passwords or contact form data), protecting it from interception. Furthermore, SSL-secured websites generate greater user trust and are ranked more favorably by Google algorithms.
Both the system itself (e.g., WordPress) and the themes and plugins used on it are constantly improved by their creators. Updates not only add new features but, above all, patch detected security holes. Leaving outdated software is the most common cause of hacks and malicious code infections.
A backup is your most important lifeline. In the event of a server crash, an update error, or a successful hacker attack, a backup allows you to restore a fully functional version of your website in moments. Backups should be performed regularly (ideally automatically every day) and stored on an external server.
First and foremost, eliminate trivial logins (such as "admin") and enforce the use of strong, unique passwords. Another crucial step is implementing two-factor authentication (2FA), changing the default login panel address, and installing a plugin that limits the number of incorrect login attempts, which protects against brute-force attacks.
Absolutely. Cheap, unproven infrastructure is vulnerable to attacks. A professional hosting provider provides the first line of defense, providing advanced web firewalls (WAF), DDoS protection, automatic backups, and regular malware scanning of server files.
Summary
The above article covers the following topics:
- how to ensure the security of your website,
- which sites are most vulnerable to attacks,
- ways to improve website security.